Bithumb2026-10-28 05:36:00Bithumb says hacked internal mobile system is separate from trading platform, probe into customer data impact continuesSouth Korean crypto exchange Bithumb said an internal mobile system used by employees for office work and communications was breached by an external party, resulting in the theft of some personal information. The exchange said it is still investigating the scope of the incident, including whether any customer information was involved. Bithumb discovered the intrusion on Oct. 27 and reported it to the Korea Internet & Security Agency and the Personal Information Protection Commission. The company said the affected internal system operates separately from its trading platform, and that the attacker could not use the breach to access customers’ crypto assets. As of now, no crypto asset losses have been reported. Bithumb has not disclosed how many people were affected or whether deposit and withdrawal services were impacted. The report was cited by CoinDesk.00
Keystone2026-10-26 14:11:34Keystone cuts customer data retention to 90 days, scraps 18,835 devices tied to old keysHardware wallet maker Keystone said its latest response to a security incident will include shorter customer data retention, the destruction of inventory tied to old verification keys, and a temporary shipping halt for certain orders. The company said the incident involved 25,964 buyer records containing personal information. It also warned that device verification keys obtained by an attacker could be used to produce counterfeit devices capable of passing checks on Keystone’s official website. In response, Keystone said it will stop using the old keys and destroy 18,835 devices in inventory that rely on them. Shipments for unfulfilled orders placed through its website have been paused and will resume after devices using new keys enter production. Keystone also said it will reduce the retention period for customer personal information from 180 days to 90 days. The company added that devices received after Oct. 20 that still use the old verification keys cannot be fully cleared of counterfeit risk even if they pass verification on the official site, and advised users to contact customer support for additional confirmation.50
Sun Yuchen2026-10-12 09:24:25Sun Yuchen and Alan Shao on AI, Crypto and Starting Over at 20MarsBit published an edited text version of a four-hour conversation between crypto entrepreneur Sun Yuchen and content creator Alan Shao, framing it around a simple question: if someone were 20 years old again, with no network, no resources and only 1,000 yuan a month to spend, how should they start over? The piece says Sun did not begin with a major, a job track or a hot sector. Instead, he laid out a personal operating system built around three ideas — “Sun studies,” “lean muscle,” and “yellow-hair thinking” — with AI added on top as a coordinating layer. The article highlights several recurring themes from the discussion. Sun argued that young people should first “AI-ify” themselves by recording their work, health and daily activity as structured data that can be stored locally and used across models through APIs. He also said AI becomes useful only after it has enough context, which means months of consistent logging rather than one-off prompts. On careers and business, he urged people to delay premature commitment, expand their sample size before choosing a direction, look for “value breaks” where supply and demand are disconnected, and think globally rather than only within a local market. The conversation also touched on freedom before wealth, the growing value of health in an AI-heavy world, the balance between conviction and “Small Ego,” and Sun’s view that crypto is building money rails machines can use directly.650
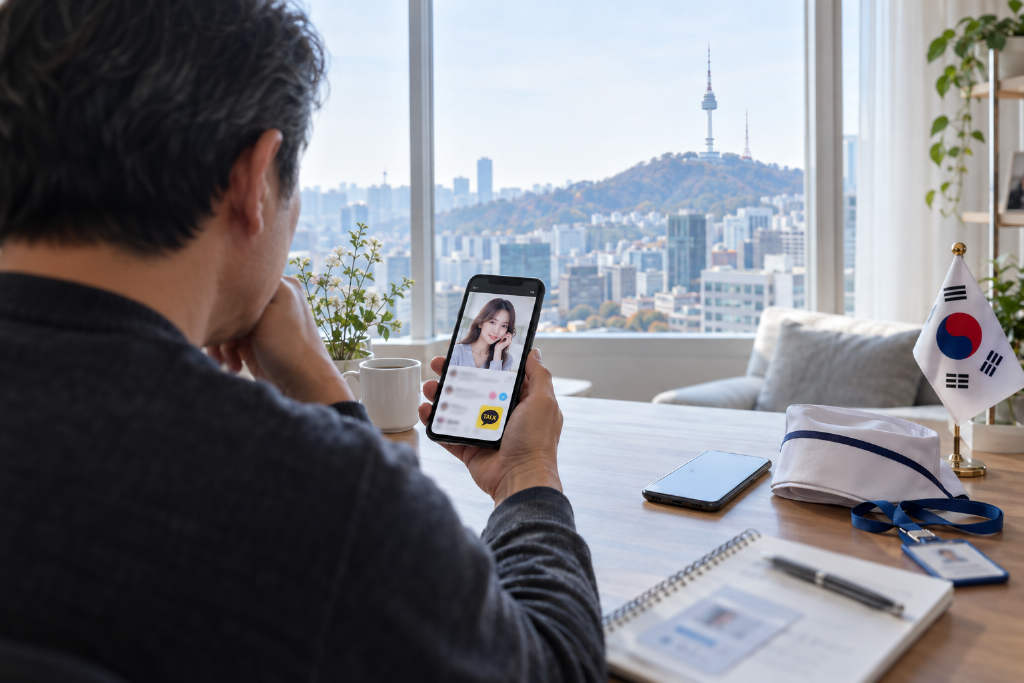
South Korea2026-10-10 07:36:02Suspected AI social media accounts in South Korea draw users into sharing personal detailsSocial platforms in South Korea are seeing a wave of accounts that local media say appear to use AI-generated profile photos and scripted personal stories to attract engagement. One of the most discussed profiles described itself as a 41-year-old nurse living in Pohang and reportedly drew comments from middle-aged and older users who openly posted their ages, locations and jobs. According to a report by Newsis on Oct. 8, the accounts typically present a ready-made persona, listing age, occupation, hobbies and relationship history before inviting conversation with lines about wanting to meet new friends or talk with similar people. The report said the images showed common signs associated with generative AI, including overly smooth skin, unnatural expressions and poses, and blurred or distorted text and small objects in the background. The report also said police are concerned such accounts could be used to build trust and later solicit money or personal information in romance scams. It did not say the accounts had already taken money or that any victim had been confirmed. Separately, statistics from South Korea’s National Police Agency showed 2,192 romance scam cases in 2025 with losses of KRW 136 billion, while 1,265 cases from February to December 2024 caused losses of KRW 67.5 billion.530
104 Job Bank2026-10-06 23:27:14104 Job Bank says unauthorized access hit about 120,000 resumes on its appTaiwan job platform 104 Job Bank said its app system detected abnormal access and an initial internal review found that about 120,000 job-seeker resumes were read without authorization. The company said it blocked the suspicious connections immediately, brought in an independent third-party cybersecurity team for digital forensics, and reported the case to regulators as well as the Taipei City field office of the Ministry of Justice Investigation Bureau. Operations across the platform remain normal, according to the company. What remains unclear is the scope of the exposed data fields. 104 said the forensic review is still underway, so it has not yet specified whether the affected records included only basic contact details such as names, phone numbers and email addresses, or whether more sensitive information such as education history, work experience, autobiographies and identification numbers was also accessed. The company said it has emailed users who may have been affected and warned members to watch for suspicious calls or messages impersonating 104 or recruiting companies.470
South Korea b2026-10-06 10:49:30South Korea says traces of Chinese-language AI hacking tool found in bank data breachesSouth Korea’s financial sector is dealing with a widening personal data breach that now spans seven financial companies, with Shinhan Bank accounting for roughly 25,000 affected individuals. According to local media reports citing the Korea Financial Security Institute, the attacks targeting Shinhan Bank, KB Kookmin Bank and Hana Bank came from nearly identical IP addresses, and investigators also found traces of an AI hacking tool developed in China and based on the Chinese language. The Financial Supervisory Service said on Oct. 6 that there were 33 attack-attempt IPs, or 28 after duplicates were removed, while cautioning that IP locations alone cannot identify the real origin because attackers may route traffic through multiple countries. On the same day, the regulator upgraded its probe into Shinhan Bank to a formal on-site inspection. Prime Minister Han Seong-sook also ordered government bodies and public institutions to immediately clean up dormant or unmanaged websites. The incident has drawn attention to exposed external systems, weak authentication controls and so-called shadow IT assets, as authorities and financial firms move into emergency inspections across the sector.570
Taiwan2026-09-18 10:33:11Taiwan cybersecurity institute deputy director indicted over 207,938 document scrapes and Azure LLM useProsecutors in Taipei have indicted four people tied to Taiwan’s National Institute of Cyber Security, including deputy director Hsu Shih-chang of its forward-looking research and procurement center, over allegations that they exploited internal system flaws to scrape official documents, personnel data, and workflow forms 207,938 times over nine months. According to the indictment, some of the scraped documents were then sent to Microsoft Azure’s large language model API to analyze procurement amounts and expected reimbursement schedules. Prosecutors said the scraping activity accounted for 85% of all document reads by institute staff and was used to build an internal budget system called XMAS. The case also alleges that after the institute cut VPN connectivity between internal and external networks in May 2025, one of the defendants used an institute-issued internal laptop with Cloudflare Tunnel to keep the crawler connected. Prosecutors said the scraped material included personal data and some classified documents, but added that there is currently no evidence the information was leaked to anyone outside current or former institute employees.830
Japan Digital2026-09-11 08:24:30Japan Digital Agency says unauthorized server access may have exposed data of about 246,000 peopleJapan’s Digital Agency said its servers were hit by unauthorized access and the personal data of about 246,000 people may have been exposed. In a statement issued on Friday, the agency said it detected in late June that someone had used a maintenance account to access a large volume of files on its Government Solutions Service Network. A follow-up investigation found that a virtual private network vulnerability may have been exploited in the intrusion. The potentially affected information belongs to civil servants and other individuals who used the system. The agency did not disclose additional details in the brief statement cited by ChainCatcher.980